Find your starting point.
Guided interviews turn what you already do into company context.
 Sinope
For startups ready for their next customer
A customer asks for certification. Get a cost breakdown built around your team.
Iceland · United Kingdom · Denmark · Finland · Norway · Sweden
Your startup. Your starting point.
Get a cost breakdown for your company, with preparation and audit costs clearly separated.
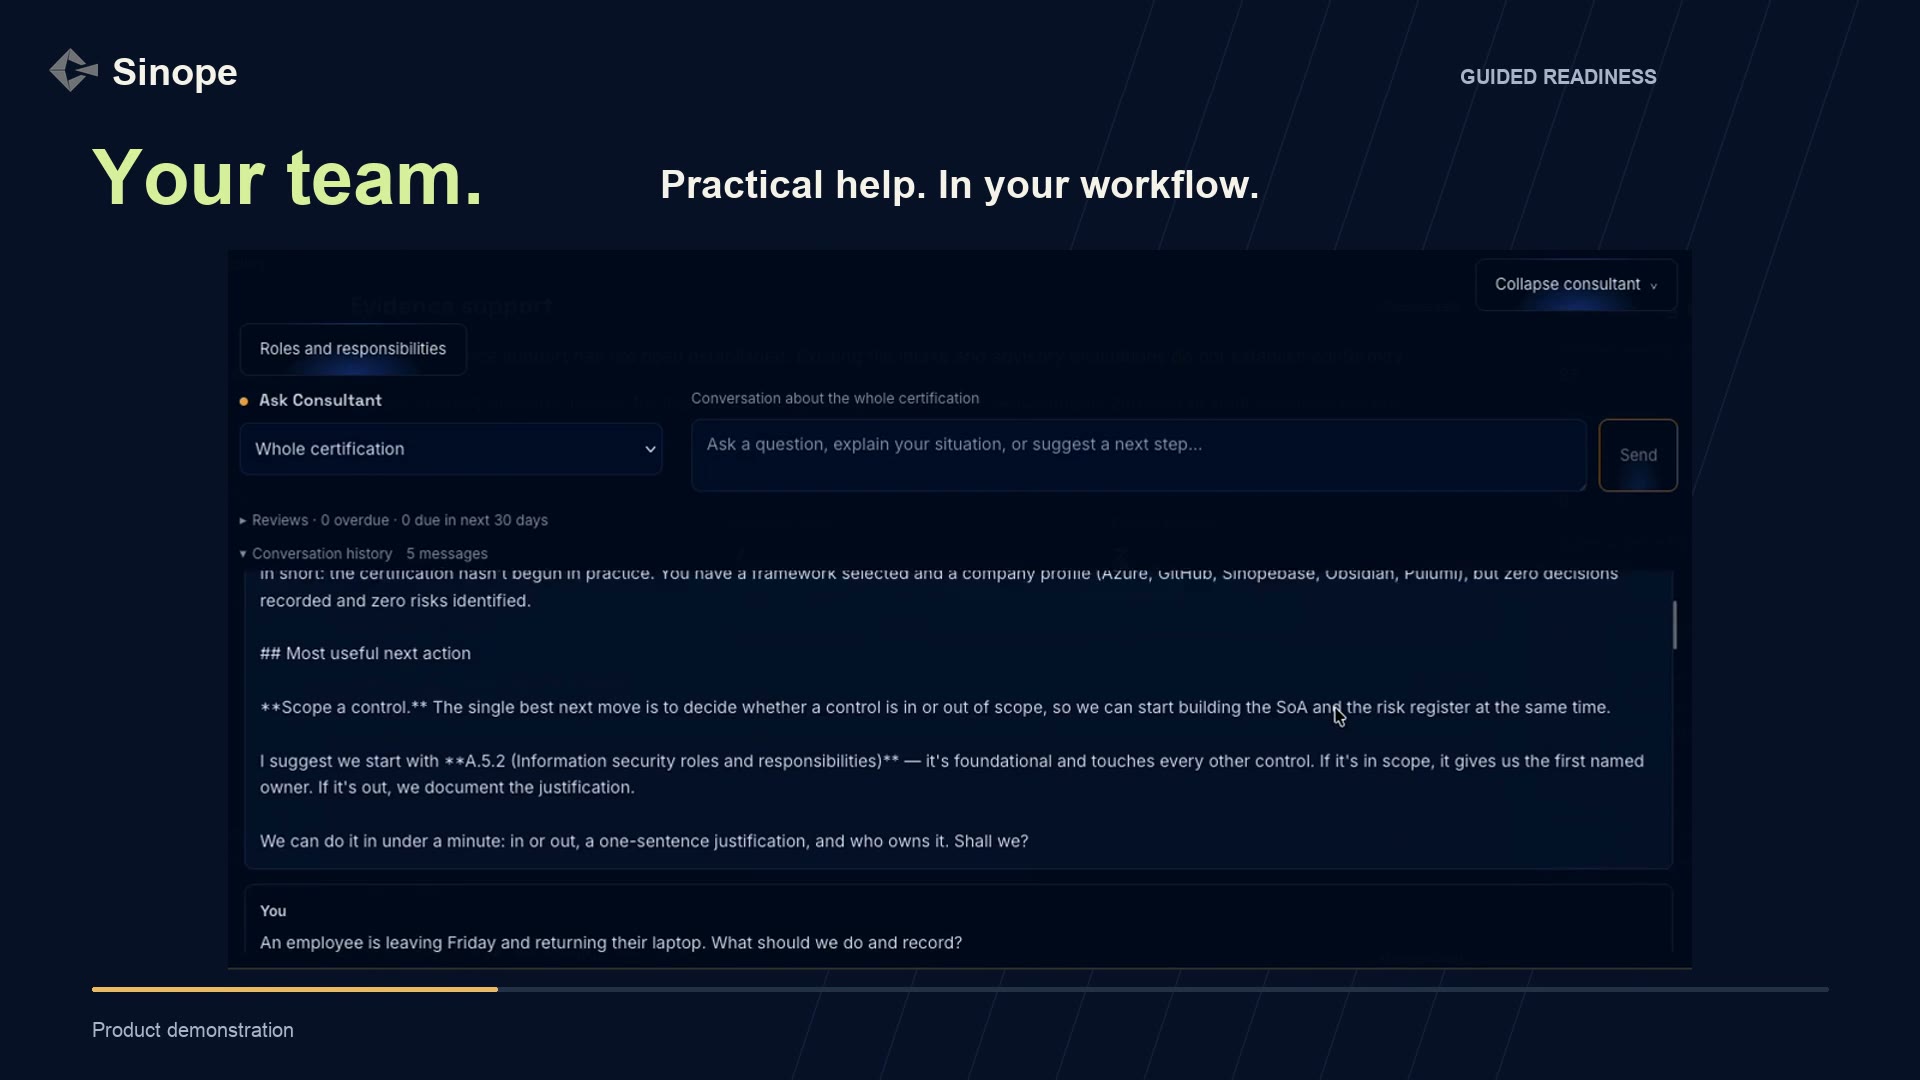
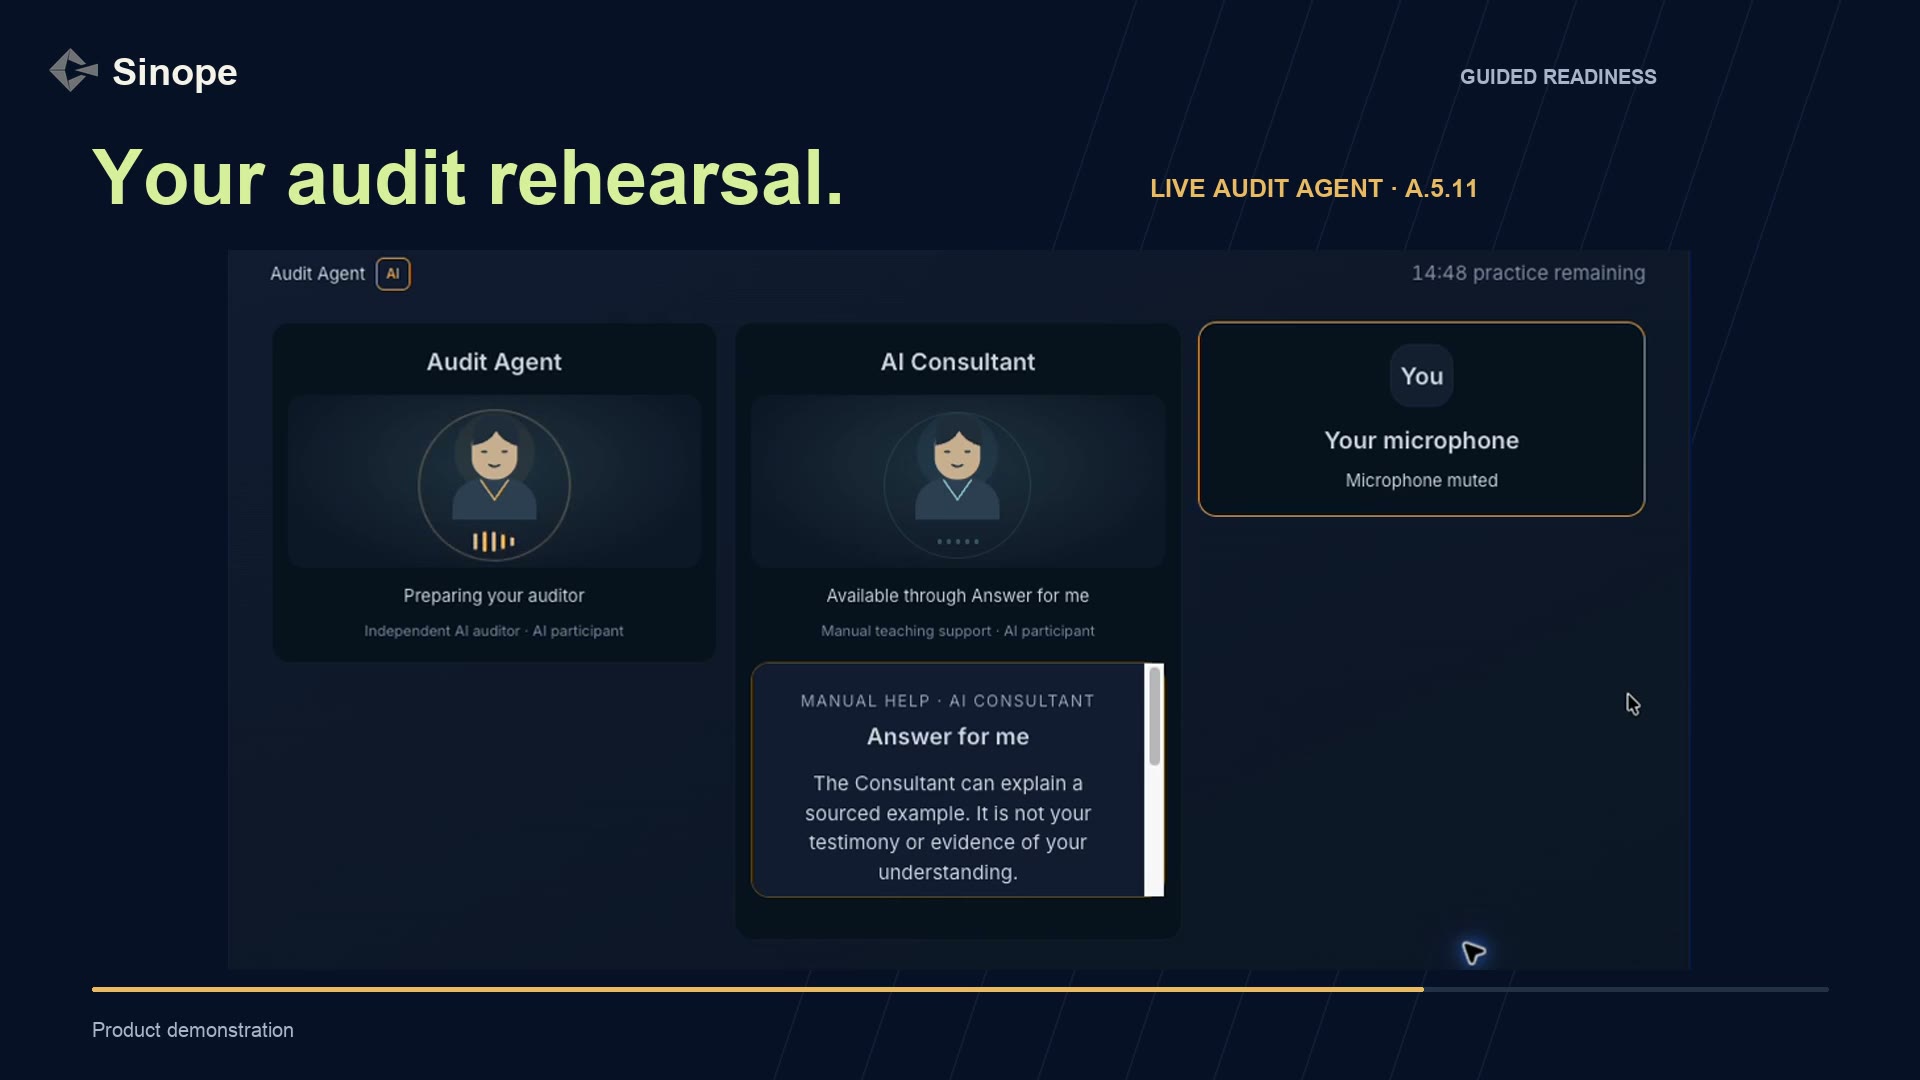
A look inside Sinope
From company context to your next step.
Product demonstration with example data. Preparation support; certification is independent.
Build for early teams landing deals.
Sinope is in development: guided preparation for startups with plenty to build.
Guided interviews turn what you already do into company context.
Organise records and review advisory assessments.
Your team owns the decisions. Certification stays independent.
A clear starting point
€5,000 EUR / target fee
Launch scope and terms are still to be confirmed. Independent audit fees and other implementation costs are separate.
A little more clarity
ISO 27001 costs depend on preparation, independent audit fees and ongoing work. Sinope targets a €5,000 EUR preparation fee. That is not the total certification cost. Request a breakdown based on your company’s size, location and starting point.
€5,000 EUR is Sinope’s target preparation fee, with final scope and terms still to be confirmed. Independent certification audits, implementation costs and your team’s time are separate. Your cost breakdown should identify these items rather than present one unexplained total.
An Icelandic startup’s ISO 27001 budget depends on its certification scope, preparation needs and the certification body’s quote. Sinope’s target preparation fee is €5,000 EUR. Request a breakdown for your company; audit fees and any applicable currency conversion remain separate.
UK teams need to budget for preparation and independent certification audits separately. Sinope’s target preparation fee is €5,000 EUR, including for UK enquiries. It is not a GBP quote. Audit pricing and any currency conversion need confirmation for your specific scope.
Team size, locations, scope and existing security practices shape the work involved for Nordic startups. A certification body quotes its audit separately. Sinope accepts enquiries from Denmark, Finland, Iceland, Norway and Sweden, with its target preparation fee stated in EUR.
Your email and cost request go to Sinope through Apollo. The team reviews the request and replies by email. The form does not issue an instant quote, calculate independent audit fees or subscribe you to a marketing sequence.
Sinope focuses on value-conscious, pre-seed startups with roughly 12–35 people. These teams need a practical way to prepare for ISO 27001 while continuing to build their business, without already having a dedicated governance, risk and compliance lead.
Sinope is compliance readiness software for AI startups, built around guided interviews and evidence review. Sinope is in development, with ISO 27001 as the first complete product focus. Teams can join the waitlist for launch updates.
ISO 27001 is the first complete product path Sinope is developing. The focus is helping teams prepare information security management records and supporting evidence. Additional frameworks are outside that first complete path and should not be assumed available.
Sinope supports preparation and does not issue ISO 27001 certificates. Certification requires an independent certification process. Interview answers, uploaded documents and advisory assessments in Sinope do not establish that an organisation has met all applicable requirements.
Sinope uses guided interviews to collect company context and discuss evidence for individual controls. The interview helps teams explain existing practices and identify information to provide. Teams remain responsible for checking that answers reflect how their organisation actually operates.
Sinope supports evidence uploads and links between evidence and controls. Teams can organise supporting material alongside their readiness work. A file being uploaded or linked does not establish its sufficiency, accuracy or acceptance by an independent auditor.
Sinope provides advisory evidence assessments to support human review. An assessment is guidance about submitted material, not an audit opinion or certification decision. Teams should review the assessment against the actual evidence, relevant scope and applicable framework criteria.
Sinope includes a downloadable control report in HTML or ZIP format. The ZIP includes an evidence manifest and original evidence files. These exports reflect current records and are transitional reports, not sealed, approved or complete audit packages.
Sinope cannot create proof that a company practice actually occurred. Teams need evidence from their own operations. Generated guidance or draft wording needs human review and must not be presented as an implemented practice without supporting facts.
Make the next step a clear one